
Before you begin
- Labs create a Google Cloud project and resources for a fixed time
- Labs have a time limit and no pause feature. If you end the lab, you'll have to restart from the beginning.
- On the top left of your screen, click Start lab to begin

Create the managementnet network
/ 20
Create the privatenet network
/ 30
Create the firewall rules for managementnet
/ 15
Create the firewall rules for privatenet
/ 15
Create the managementnet-vm instance
/ 5
Create the privatenet-vm instance
/ 5
Create a VM instance with multiple network interfaces
/ 10
Create the managementnet network
/ 20
Create the privatenet network
/ 30
Create the firewall rules for managementnet
/ 15
Create the firewall rules for privatenet
/ 15
Create the managementnet-vm instance
/ 5
Create the privatenet-vm instance
/ 5
Create a VM instance with multiple network interfaces
/ 10


Virtual Private Cloud (VPC) networks allow you to maintain isolated environments within a larger cloud structure, giving you granular control over data protection, network access, and application security.
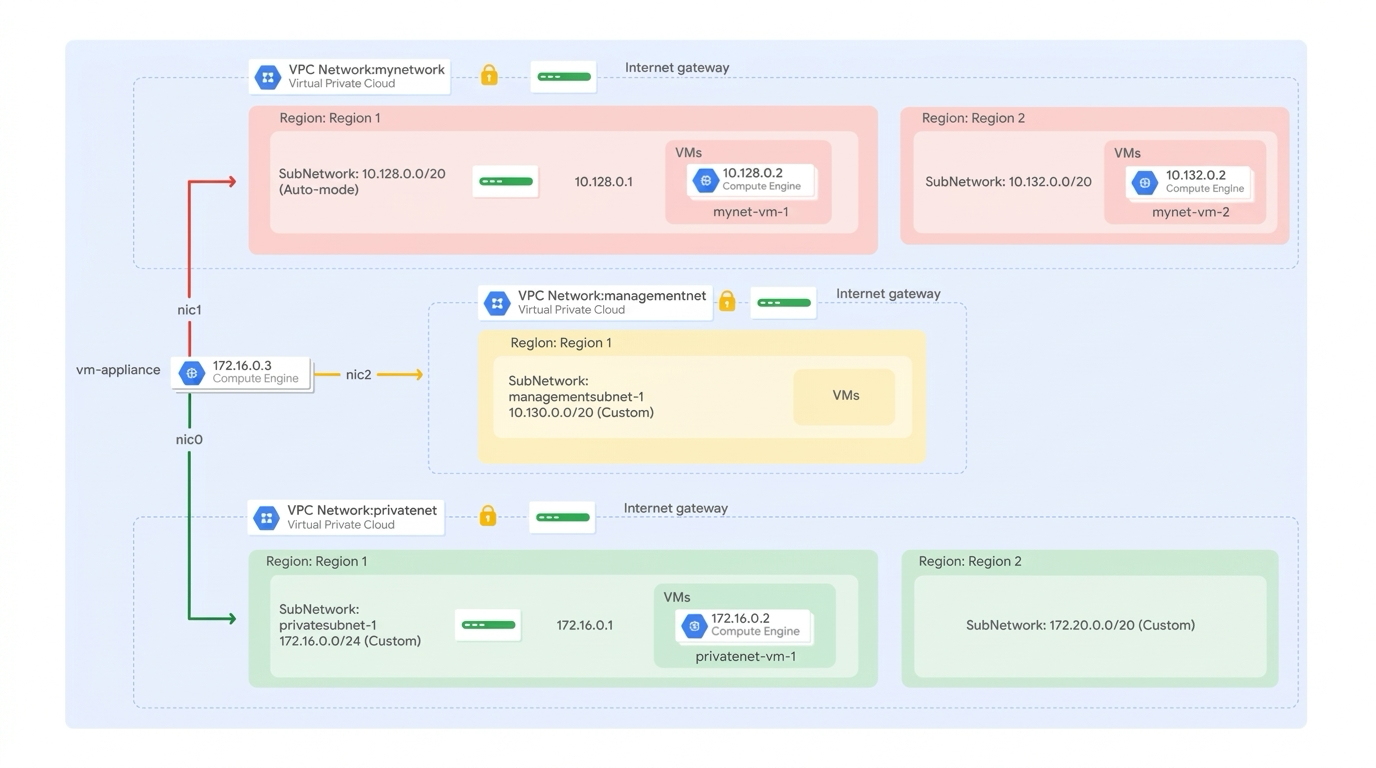
In this lab, you create several VPC networks and VM instances, and then test connectivity across networks. Specifically, you create two custom mode networks (managementnet and privatenet) with firewall rules and VM instances as shown in this network diagram:
The mynetwork network, its firewall rules, and two VM instances (mynet-vm-1 and mynet-vm-2) already exist in your project for this lab.
In this lab, you learn how to perform the following tasks:
Read these instructions. Labs are timed and you cannot pause them. The timer, which starts when you click Start Lab, shows how long Google Cloud resources are made available to you.
This hands-on lab lets you do the lab activities in a real cloud environment, not in a simulation or demo environment. It does so by giving you new, temporary credentials you use to sign in and access Google Cloud for the duration of the lab.
To complete this lab, you need:
Click the Start Lab button. If you need to pay for the lab, a dialog opens for you to select your payment method. On the right is the Lab setup and access panel with the following:
Note that the lab timer is located near the top of the page, showing the remaining time.
Click Open Google Cloud console (or right-click and select Open Link in Incognito Window if you are running the Chrome browser).
The lab spins up resources, and then opens another tab that shows the Sign in page.
Tip: Arrange the tabs in separate windows, side-by-side.
If necessary, copy the Username below and paste it into the Sign in dialog.
You can also find the Username in the Lab setup and access panel.
Click Next.
Copy the Password below and paste it into the Welcome dialog.
You can also find the Password in the Lab setup and access panel.
Click Next.
Click through the subsequent pages:
After a few moments, the Google Cloud console opens in this tab.

Cloud Shell is a virtual machine that is loaded with development tools. It offers a persistent 5GB home directory and runs on the Google Cloud. Cloud Shell provides command-line access to your Google Cloud resources.
Click Activate Cloud Shell 
Click through the following windows:
When you are connected, you are already authenticated, and the project is set to your Project_ID,
gcloud is the command-line tool for Google Cloud. It comes pre-installed on Cloud Shell and supports tab-completion.
Output:
Output:
gcloud, in Google Cloud, refer to the gcloud CLI overview guide.
Create two custom networks, managementnet and privatenet, along with firewall rules to allow SSH, ICMP, and RDP ingress traffic.
Create the managementnet network using the Google Cloud console.
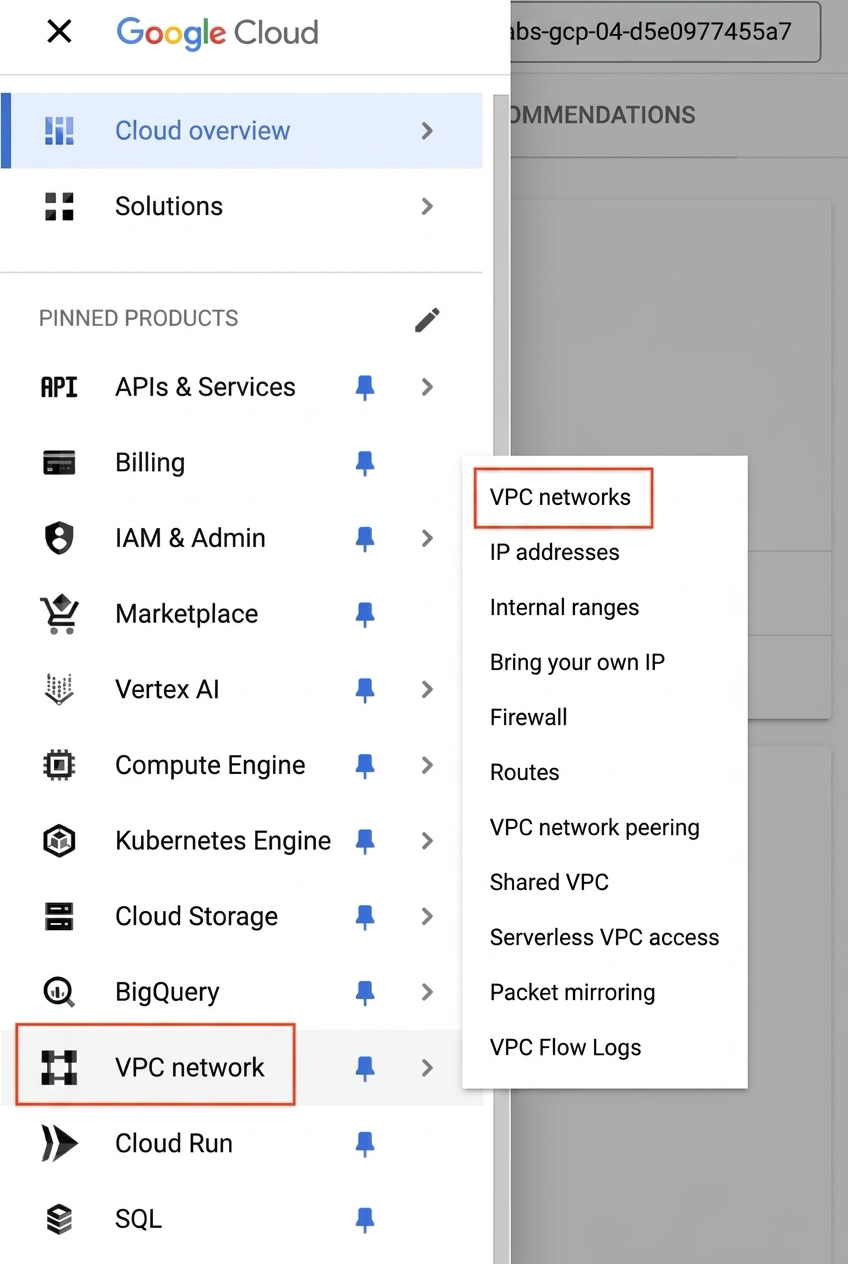
In the Google Cloud console, on the Navigation menu (
Notice the default and mynetwork networks with their subnets. Each Google Cloud project starts with the default network. In addition, your project includes the preconfigured mynetwork network as part of your network diagram.
Click Create VPC network.
For Name, type managementnet
For Subnet creation mode, select Custom.
In the New subnet section, specify the following, and leave the remaining settings as their defaults:
| Property | Value (type value or select option as specified) |
|---|---|
| Name | managementsubnet-1 |
| Region | |
| IPv4 range | 10.130.0.0/20 |
Click Done.
Click Equivalent command line.
These commands illustrate that you can create networks and subnets using the Cloud Shell command line. You create the privatenet network using these commands with similar parameters.
Click Close.
Click Create.
Click Check my progress to verify the objective.
Create the privatenet network using the Cloud Shell command line.
privatenet network:privatesubnet-1 subnet:privatesubnet-2 subnet:Click Check my progress to verify the objective.
The output should look like this:
default and mynetwork are auto mode networks, whereas managementnet and privatenet are custom mode networks. Auto mode networks create subnets in each region automatically, whereas custom mode networks start with no subnets, giving you full control over subnet creation.
The output should look like this:
default and mynetwork networks have subnets in each Google Cloud region (zones and regions might vary based on the lab's requirements) because they are auto mode networks. The managementnet and privatenet networks only have the subnets that you created because they are custom mode networks.
In the Google Cloud console, on the Navigation menu (
The same networks and subnets appear in the Google Cloud console.
Create firewall rules to allow SSH, ICMP, and RDP ingress traffic to VM instances on the managementnet network.
In the Google Cloud console, on the Navigation menu (
Click Create firewall rule.
Specify the following, and leave the remaining settings as their defaults:
| Property | Value (type value or select option as specified) |
|---|---|
| Name | managementnet-allow-icmp-ssh-rdp |
| Network | managementnet |
| Targets | All instances in the network |
| Source filter | IPv4 ranges |
| Source IPv4 ranges | 0.0.0.0/0 |
| Protocols and ports | Select Specified protocols and ports, select TCP and type 22, 3389, and then select Other protocols and type icmp |
/0 in the Source IPv4 ranges field to specify all networks.
Click Equivalent command line.
These commands illustrate that you can also create firewall rules using the Cloud Shell command line. You create the firewall rules for privatenet using these commands with similar parameters.
Click Close.
Click Create.
Click Check my progress to verify the objective.
Create the firewall rules for the privatenet network using the Cloud Shell command line.
privatenet-allow-icmp-ssh-rdp firewall rule:The output should look like this:
Click Check my progress to verify the objective.
The output should look like this:
The firewall rules for the mynetwork network already exist in your project. You can define multiple protocols and ports in one firewall rule (privatenet and managementnet), or spread them across multiple rules (default and mynetwork).
In the Google Cloud console, on the Navigation menu (
The same firewall rules appear in the Google Cloud console.
Create two VM instances:
managementnet-vm-1 in managementsubnet-1
privatenet-vm-1 in privatesubnet-1
Create the managementnet-vm-1 instance using the Google Cloud console.
In the Google Cloud console, on the Navigation menu (
The mynet-vm-1 and mynet-vm-2 instances already exist in your project as part of your network diagram.
Click Create instance.
In the Machine configuration section, specify the following, and leave the remaining settings as their defaults:
| Property | Value (type value or select option as specified) |
|---|---|
| Name | managementnet-vm-1 |
| Region | |
| Zone | |
| Series | E2 |
| Machine type | e2-micro |
Click Networking.
For Network interfaces, expand the default interface to edit it, specify the following, and leave the remaining settings as their defaults:
| Property | Value (type value or select option as specified) |
|---|---|
| Network | managementnet |
| Subnetwork | managementsubnet-1 |
Click Done.
Click Equivalent code.
This illustrates that you can also create VM instances using the Cloud Shell command line. You create the privatenet-vm-1 instance using these commands with similar parameters.
Click Create.
Click Check my progress to verify the objective.
Create the privatenet-vm-1 instance using the Cloud Shell command line.
privatenet-vm-1 instance:The output should look like this:
Click Check my progress to verify the objective.
The output should look like this:
In the Google Cloud console, on the Navigation menu (
The VM instances appear in the Google Cloud console.
Click Column display options, select Network, and then click OK.
There are three instances in managementnet, mynetwork, and privatenet), with no instance in the same zone and network as another. In the next section, you explore the effect this has on internal connectivity.
Explore the connectivity between the VM instances. Specifically, determine the effect of having VM instances in the same zone versus having instances in the same VPC network.
Ping the external IP addresses of the VM instances to determine whether you can reach the instances from the public internet.
In the Google Cloud console, on the Navigation menu (
Note the external IP addresses for mynet-vm-2, managementnet-vm-1, and privatenet-vm-1.
For mynet-vm-1, click SSH to launch a terminal and connect.
To test connectivity to the external IP address of mynet-vm-2, run the following command, replacing the placeholder with the external IP address of mynet-vm-2:
This should work!
managementnet-vm-1, run the following command, replacing the placeholder with the external IP address of managementnet-vm-1:This should work!
privatenet-vm-1, run the following command, replacing the placeholder with the external IP address of privatenet-vm-1:This should work!
Ping the internal IP addresses of the VM instances to determine whether you can reach the instances from within a VPC network.
), click Compute Engine > VM instances.mynet-vm-2, managementnet-vm-1, and privatenet-vm-1.mynet-vm-1.mynet-vm-2, run the following command, replacing the placeholder with the internal IP address of mynet-vm-2:mynet-vm-2 because it is on the same VPC network as the source of the ping (mynet-vm-1), even though both VM instances are in separate zones, regions, and continents!
managementnet-vm-1, run the following command, replacing the placeholder with the internal IP address of managementnet-vm-1:privatenet-vm-1, run the following command, replacing the placeholder with the internal IP address of privatenet-vm-1:managementnet-vm-1 and privatenet-vm-1 because they are in separate VPC networks from the source of the ping (mynet-vm-1), even though they are all in the same region (VPC networks are by default isolated private networking domains. However, Google Cloud does not allow internal IP address communication between networks unless you set up mechanisms such as VPC Network Peering or Cloud VPN.
region_1 = region_2 = Every instance in a VPC network has a default network interface. You can create additional network interfaces attached to your VMs. Multiple network interfaces enable you to create configurations in which an instance connects directly to several VPC networks (up to eight interfaces, depending on the instance's type).
Create the vm-appliance instance with network interfaces in privatesubnet-1, managementsubnet-1, and mynetwork. The CIDR ranges of these subnets do not overlap, which is a requirement for creating a VM with multiple network interface controllers (NICs).
In the Google Cloud console, on the Navigation menu (
Click Create instance.
In the Machine configuration section, specify the following, and leave the remaining settings as their defaults:
| Property | Value (type value or select option as specified) |
|---|---|
| Name | vm-appliance |
| Region | |
| Zone | |
| Series | E2 |
| Machine type | e2-standard-4 |
e2-standard-4 machine type allows up to four network interfaces. Refer to the Maximum number of network interfaces section of the Google Cloud VPC documentation for more information.
Click Networking.
For Network interfaces, expand the default interface to edit it, specify the following, and leave the remaining settings as their defaults:
| Property | Value (type value or select option as specified) |
|---|---|
| Network | privatenet |
| Subnetwork | privatesubnet-1 |
Click Done.
Click Add a network interface, specify the following, and leave the remaining settings as their defaults:
| Property | Value (type value or select option as specified) |
|---|---|
| Network | managementnet |
| Subnetwork | managementsubnet-1 |
Click Done.
Click Add a network interface, specify the following, and leave the remaining settings as their defaults:
| Property | Value (type value or select option as specified) |
|---|---|
| Network | mynetwork |
| Subnetwork | mynetwork |
Click Done.
Click Create.
Click Check my progress to verify the objective.
Explore the network interface details of vm-appliance within the Google Cloud console and within the VM's terminal.
In the Google Cloud console, on the Navigation menu (
In the Internal IP column for vm-appliance, click nic0 to open the Network interface details page.
Verify that nic0 connects to privatesubnet-1, has an internal IP address within that subnet (172.16.0.0/24), and applies the relevant firewall rules.
Click nic0, and then select nic1.
Verify that nic1 connects to managementsubnet-1, has an internal IP address within that subnet (10.130.0.0/20), and applies the relevant firewall rules.
Click nic1, and then select nic2.
Verify that nic2 connects to mynetwork, has an internal IP address within that subnet (10.128.0.0/20), and applies the relevant firewall rules.
), click Compute Engine > VM instances.The output should look like this:
sudo ifconfig command lists a Linux VM's network interfaces along with the internal IP addresses for each interface.
Demonstrate that the vm-appliance instance connects to privatesubnet-1, managementsubnet-1, and mynetwork by pinging VM instances on those subnets.
), click Compute Engine > VM instances.privatenet-vm-1, managementnet-vm-1, mynet-vm-1, and mynet-vm-2.vm-appliance.privatenet-vm-1, run the following command, replacing the placeholder with the internal IP address of privatenet-vm-1:This works!
privatenet-vm-1 by its name because VPC networks have an internal DNS service that allows you to address instances by their DNS names rather than their internal IP addresses. When you make an internal DNS query with the instance hostname, it resolves to the primary interface (nic0) of the instance. Therefore, this only works for privatenet-vm-1 in this case.
managementnet-vm-1, run the following command, replacing the placeholder with the internal IP address of managementnet-vm-1:This works!
mynet-vm-1, run the following command, replacing the placeholder with the internal IP address of mynet-vm-1:This works!
mynet-vm-2, run the following command, replacing the placeholder with the internal IP address of mynet-vm-2:eth0. Unless you manually configure it otherwise, any traffic leaving an instance for any destination other than a directly connected subnet leaves the instance via the default route on eth0.
vm-appliance instance, run the following command:The output should look like this:
eth0 gets the default route (default via 172.16.0.1 dev eth0), and all three interfaces (eth0, eth1, and eth2) get routes for their respective subnets. Because this routing table does not include the subnet of mynet-vm-2 (10.132.0.0/20), the ping to that instance leaves vm-appliance on eth0 (which is on a different VPC network). You can change this behavior by configuring policy routing as documented in the Configuring policy routing section of the Google Cloud VPC documentation.
In this lab, you created a VM instance with three network interfaces and verified internal connectivity for VM instances that are on the subnets that are attached to the multiple interface VM.
You also explored the default network along with its subnets, routes, and firewall rules. You then created custom mode VPC networks and tested connectivity across them.
To learn more about VPC networking, see Using VPC Networks.
...helps you make the most of Google Cloud technologies. Our classes include technical skills and best practices to help you get up to speed quickly and continue your learning journey. We offer fundamental to advanced level training, with on-demand, live, and virtual options to suit your busy schedule. Certifications help you validate and prove your skill and expertise in Google Cloud technologies.
Manual Last Updated on November 13, 2026
Lab Last Tested September 2, 2026
Copyright 2026 Google LLC. All rights reserved. Google and the Google logo are trademarks of Google LLC. All other company and product names may be trademarks of the respective companies with which they are associated.



This content is not currently available
We can notify you via email when it becomes available

Great!
We can contact you via email if it becomes available


One lab at a time
Confirm to end all existing labs and start this one