
Create a custom network in project A

Check my progress

/ 20

Create a custom network in project B

Check my progress

/ 20

Peer network-a with network-b

Check my progress

/ 30

Peer network-b with network-a

Check my progress

/ 30

This lab may incorporate AI tools to support your learning.
This content is not yet optimized for mobile devices.
For the best experience, please visit us on a desktop computer using a link sent by email.

GSP193

Google Cloud self-paced labs

Overview

Google Cloud Virtual Private Cloud (VPC) Network Peering allows private connectivity across two VPC networks regardless of whether they belong to the same project or the same organization.

VPC Network Peering allows you to build SaaS (Software-as-a-Service) ecosystems in Google Cloud, making services available privately across different VPC networks within and across organizations, allowing workloads to communicate in private space.

VPC Network Peering is useful for:

  • Organizations with several network administrative domains.
  • Organizations that want to peer with other organizations.

If you have multiple network administrative domains within your organization, VPC Network Peering allows you to make services available across VPC networks in private space. If you offer services to other organizations, VPC Network Peering allows you to make those services available in private space to those organizations.

The ability to offer services across organizations is useful if you want to offer services to other enterprises, and it is useful within your own enterprise if you have several distinct organization nodes due to your own structure or as a result of mergers or acquisitions.

VPC Network Peering gives you several advantages over using external IP addresses or VPNs to connect networks, including:

  • Network latency: Private networking offers lower latency than public IP networking.
  • Network security: Service owners do not need to expose their services to the public internet and deal with its associated risks.
  • Network cost: Peered networks can use internal IPs to communicate and save Google Cloud egress bandwidth costs. Regular network pricing still applies to all traffic.

What you'll learn

In this lab, you learn how to perform the following tasks:

  • Create a custom VPC network in two projects.
  • Set up a VPC Network Peering session.
  • Test connectivity between peered networks.

Setup and requirements

Before you click the Start Lab button

Read these instructions. Labs are timed and you cannot pause them. The timer, which starts when you click Start Lab, shows how long Google Cloud resources are made available to you.

This hands-on lab lets you do the lab activities in a real cloud environment, not in a simulation or demo environment. It does so by giving you new, temporary credentials you use to sign in and access Google Cloud for the duration of the lab.

To complete this lab, you need:

  • Access to a standard internet browser (Chrome browser recommended).
Note: Use an Incognito (recommended) or private browser window to run this lab. This prevents conflicts between your personal account and the student account, which may cause extra charges incurred to your personal account.
  • Time to complete the lab—remember, once you start, you cannot pause a lab.
Note: Use only the student account for this lab. If you use a different Google Cloud account, you may incur charges to that account.

How to start your lab and sign in to the Google Cloud console

  1. Click the Start Lab button. If you need to pay for the lab, a dialog opens for you to select your payment method. On the right is the Lab setup and access panel with the following:

    • The Open Google Cloud console button
    • The temporary credentials (username and password) that you must use for this lab
    • Other information, if needed, to step through this lab

    Note that the lab timer is located near the top of the page, showing the remaining time.

  2. Click Open Google Cloud console (or right-click and select Open Link in Incognito Window if you are running the Chrome browser).

    The lab spins up resources, and then opens another tab that shows the Sign in page.

    Tip: Arrange the tabs in separate windows, side-by-side.

    Note: If you see the Choose an account dialog, click Use Another Account.
  3. If necessary, copy the Username below and paste it into the Sign in dialog.

    {{{user_0.username | "Username"}}}

    You can also find the Username in the Lab setup and access panel.

  4. Click Next.

  5. Copy the Password below and paste it into the Welcome dialog.

    {{{user_0.password | "Password"}}}

    You can also find the Password in the Lab setup and access panel.

  6. Click Next.

    Important: You must use the credentials the lab provides you. Do not use your Google Cloud account credentials. Note: Using your own Google Cloud account for this lab may incur extra charges.
  7. Click through the subsequent pages:

    • Accept the terms and conditions.
    • Do not add recovery options or two-factor authentication (because this is a temporary account).
    • Do not sign up for free trials.

After a few moments, the Google Cloud console opens in this tab.

Note: To access Google Cloud products and services, click the Navigation menu or type the service or product name in the Search field. Navigation menu icon and Search field

Activate Cloud Shell

Cloud Shell is a virtual machine that is loaded with development tools. It offers a persistent 5GB home directory and runs on the Google Cloud. Cloud Shell provides command-line access to your Google Cloud resources.

  1. Click Activate Cloud Shell Activate Cloud Shell icon at the top of the Google Cloud console.

  2. Click through the following windows:

    • Continue through the Cloud Shell information window.
    • Authorize Cloud Shell to use your credentials to make Google Cloud API calls.

When you are connected, you are already authenticated, and the project is set to your Project_ID, . The output contains a line that declares the Project_ID for this session:

Your Cloud Platform project in this session is set to {{{project_0.project_id | "PROJECT_ID"}}}

gcloud is the command-line tool for Google Cloud. It comes pre-installed on Cloud Shell and supports tab-completion.

  1. (Optional) You can list the active account name with this command:
gcloud auth list
  1. Click Authorize.

Output:

ACTIVE: * ACCOUNT: {{{user_0.username | "ACCOUNT"}}} To set the active account, run: $ gcloud config set account `ACCOUNT`
  1. (Optional) You can list the project ID with this command:
gcloud config list project

Output:

[core] project = {{{project_0.project_id | "PROJECT_ID"}}} Note: For full documentation of gcloud, in Google Cloud, refer to the gcloud CLI overview guide.

Task 1. Create a custom network in both projects

Within the same organization node, a network can host services that need to be accessible from other VPC networks in the same or different projects.

Alternatively, one organization might want to access services that a third party offers.

Project names are unique across all of Google Cloud, so you do not need to specify the organization when setting up peering. Google Cloud knows the organization based on the project name.

In this lab, you use two provisioned projects: the first project is project-A, and the second project is project-B.

Configure your Cloud Shell environment

  1. To open a second Cloud Shell tab, in the Cloud Shell toolbar, click Open a new tab (+).

  2. In the first Cloud Shell tab (for project-A), run the following command to set the project ID for project-A:

gcloud config set project {{{project_0.project_id | Project ID 1}}}
  1. In the second Cloud Shell tab (for project-B), run the following command to set the project ID for project-B:
gcloud config set project {{{project_1.project_id | Project ID 2}}}

Create the custom network and VM in project-A

  1. Return to the first Cloud Shell tab, and run the following command to create a custom network:
gcloud compute networks create network-a --subnet-mode custom
  1. Run the following command to create a subnet within this VPC network and specify a region and IP range:
gcloud compute networks subnets create network-a-subnet --network network-a \ --range 10.0.0.0/16 --region {{{ project_0.default_region | "REGION 1" }}}
  1. Run the following command to create a VM instance:
gcloud compute instances create vm-a --zone {{{ project_0.default_zone | "ZONE 1" }}} --network network-a --subnet network-a-subnet --machine-type e2-small
  1. Run the following command to enable SSH and icmp firewall rules, because you need a secure shell to communicate with VMs during connectivity testing:
gcloud compute firewall-rules create network-a-fw --network network-a --allow tcp:22,icmp

Next, you set up project-B in the same way.

Click Check my progress to verify the objective. Create a custom network in project-A

Create the custom network and VM in project-B

  1. Switch to the second Cloud Shell tab, and run the following command to create a custom network:
gcloud compute networks create network-b --subnet-mode custom
  1. Run the following command to create a subnet within this VPC network and specify a region and IP range:
gcloud compute networks subnets create network-b-subnet --network network-b \ --range 10.8.0.0/16 --region {{{ project_1.default_region | "REGION 2"}}}
  1. Run the following command to create a VM instance:
gcloud compute instances create vm-b --zone {{{ project_1.default_zone | "ZONE 2"}}} --network network-b --subnet network-b-subnet --machine-type e2-small
  1. Run the following command to enable SSH and icmp firewall rules, because you need a secure shell to communicate with VMs during connectivity testing:
gcloud compute firewall-rules create network-b-fw --network network-b --allow tcp:22,icmp

Click Check my progress to verify the objective. Create a custom network in project-B

Task 2. Set up a VPC network peering session

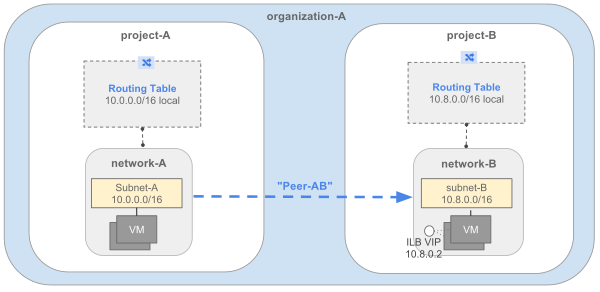
Consider an organization that needs to establish VPC Network Peering between network-a in project-A and network-b in project-B. To establish VPC Network Peering successfully, administrators of network-a and network-b must separately configure the peering association.

Peer network-a with network-b

Peer-AB network diagram

  1. In the Google Cloud console, click the project selector menu in the top bar.

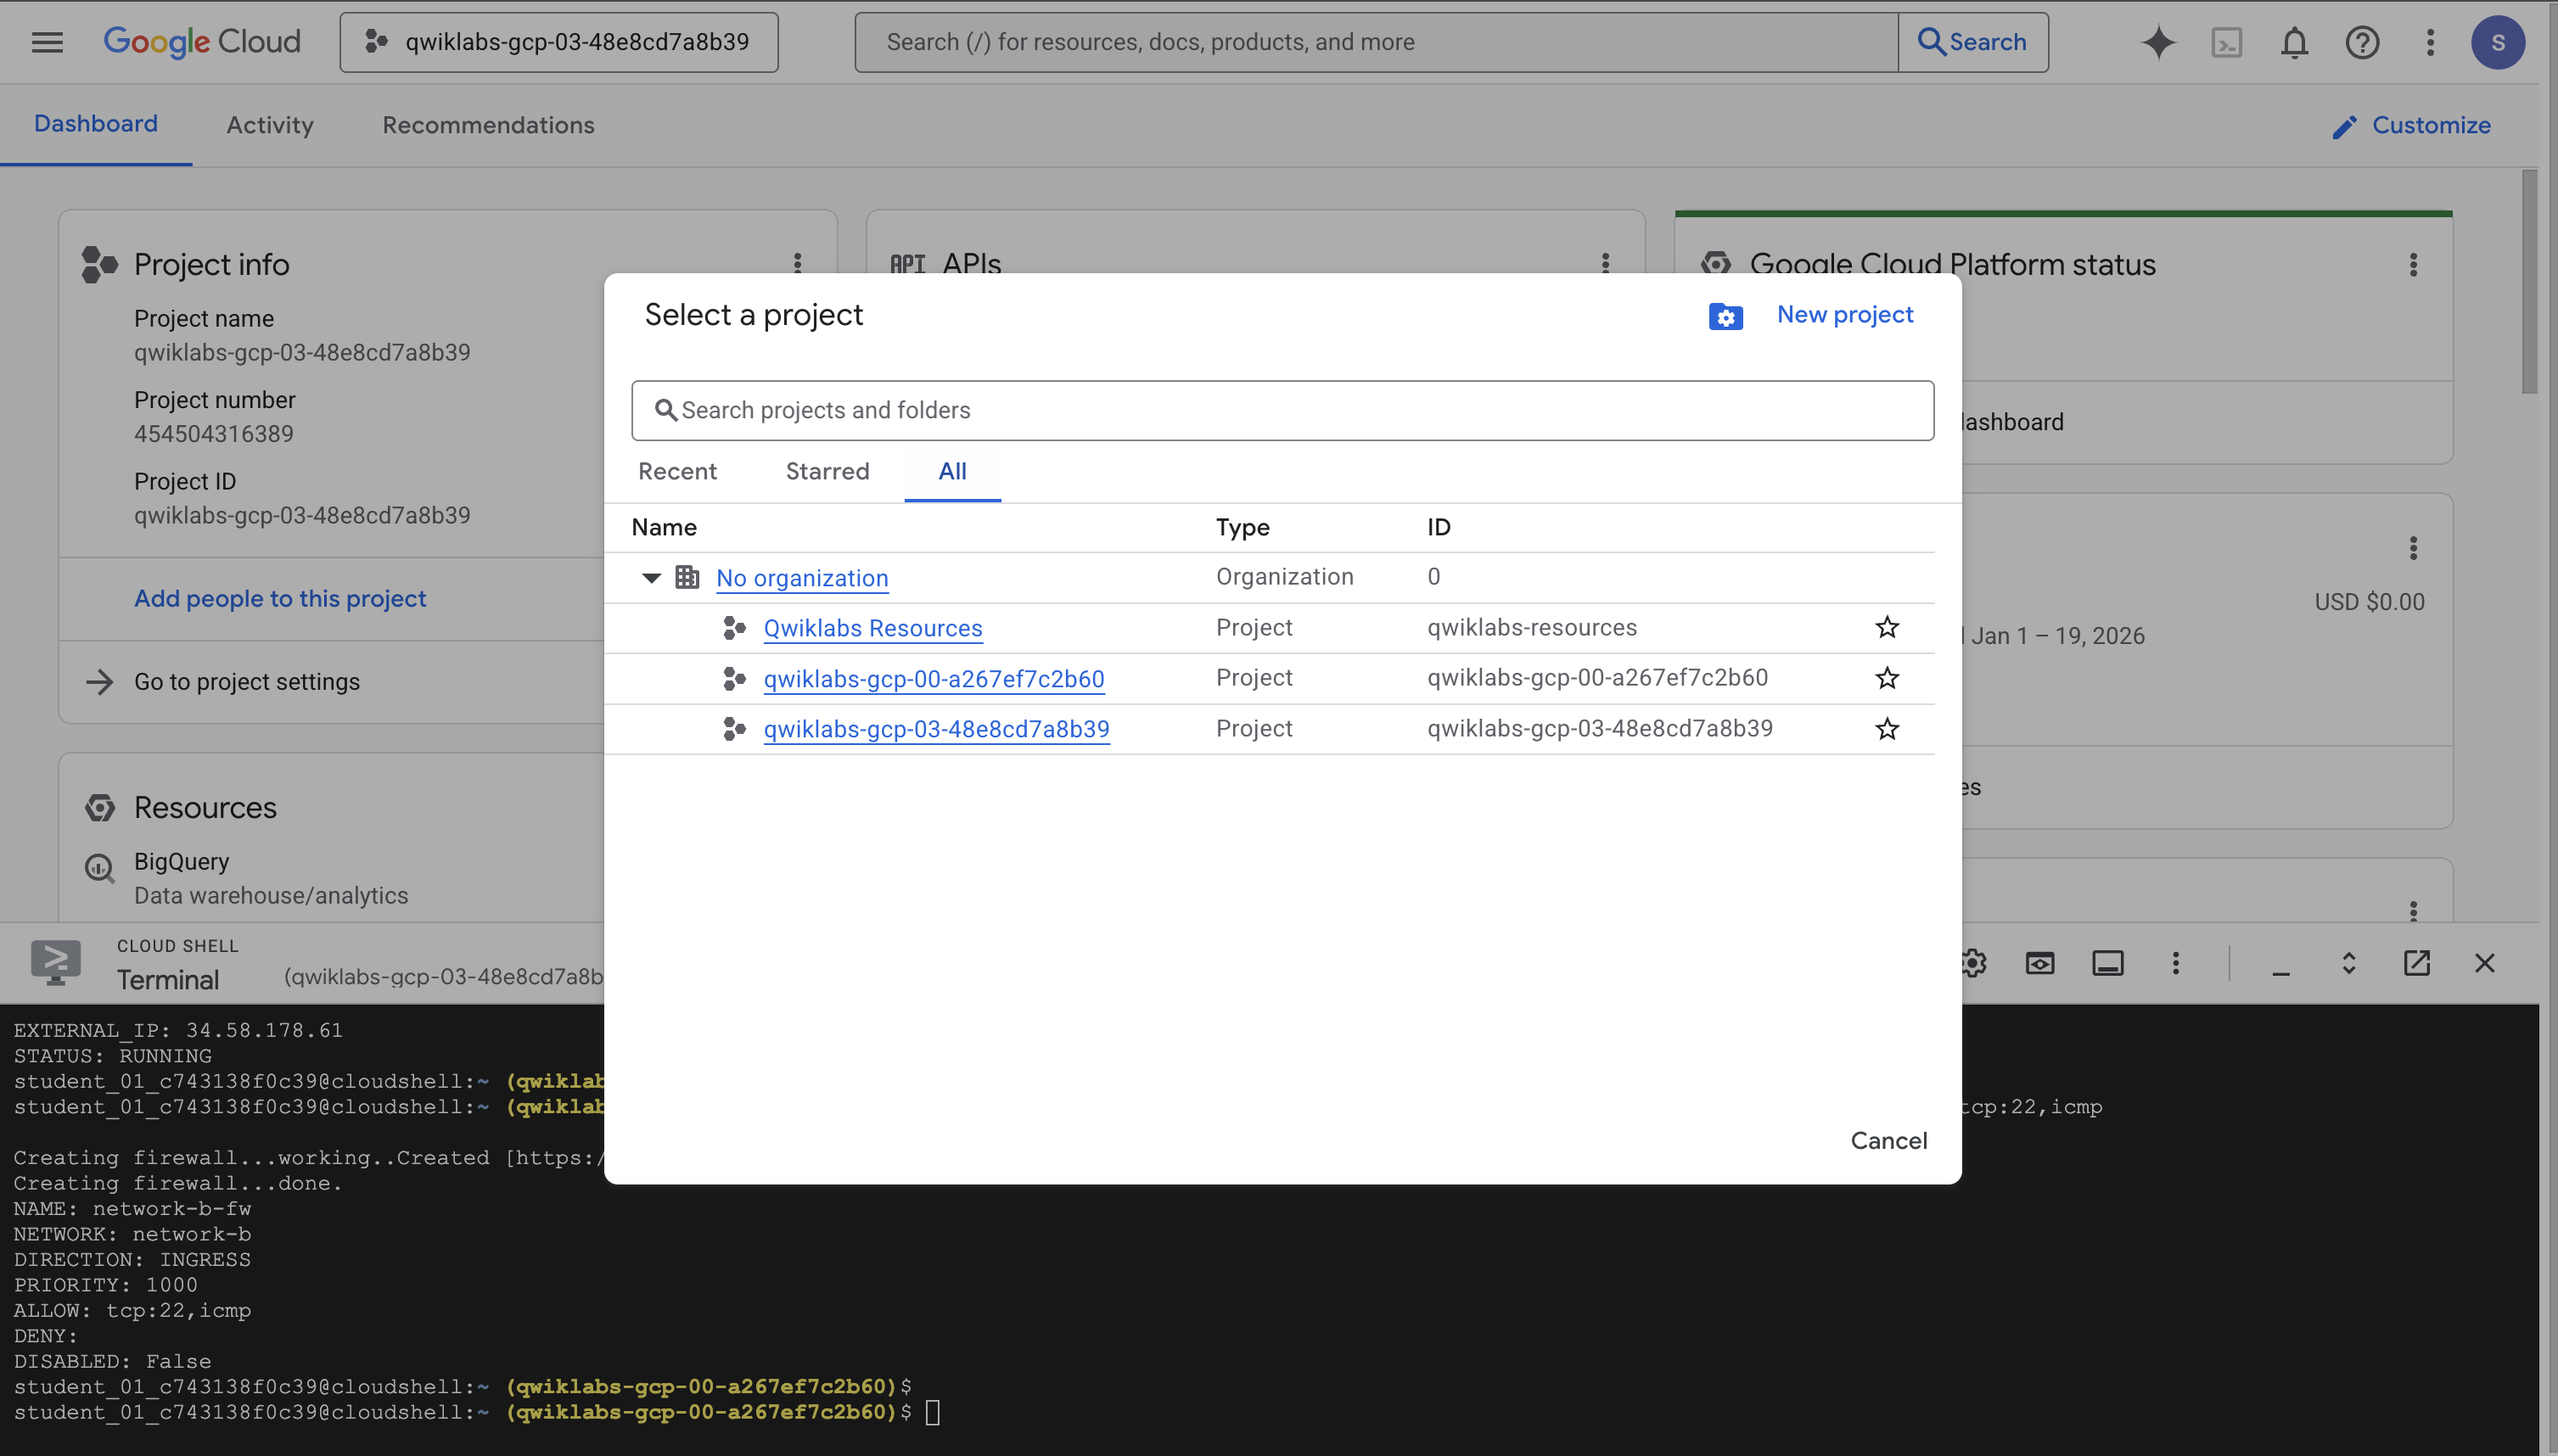
  2. In the Select a project dialog, click the All tab, and then select (project-A).

Select project dialog box

  1. On the Navigation menu (Navigation menu icon), click VPC network > VPC network peering.

  2. Click Create connection.

  3. Click Continue.

  4. For Name, type peer-ab

  5. For Your VPC network, select network-a.

  6. For Peered VPC network, select In another project.

  7. For Project ID, paste the project ID of the second project (project-B):

{{{ project_1.project_id | "PROJECT ID 2"}}}
  1. For VPC network name, type network-b

  2. Click Create.

At this point, the peering state remains INACTIVE because there is no matching configuration in network-b in project-B. The Status column displays the message Waiting for the connection to be created by network-b.

Click Check my progress to verify the objective. Peer network-a with network-b

Peer network-b with network-a

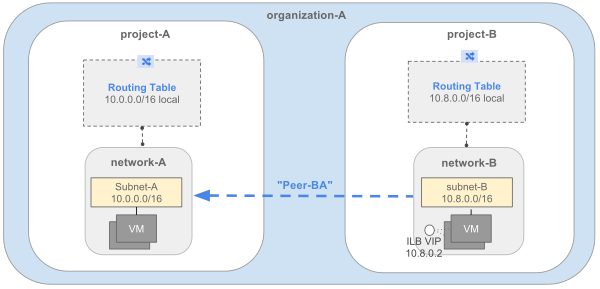
Peer-BA network diagram

Note: Switch to the second project (project-B) in the Google Cloud console before creating the peering connection.
  1. In the Google Cloud console, click the project selector menu in the top bar, click the All tab, and then select (project-B).

  2. On the Navigation menu (Navigation menu icon), click VPC network > VPC network peering.

  3. Click Create connection.

  4. Click Continue.

  5. For Name, type peer-ba

  6. For Your VPC network, select network-b.

  7. For Peered VPC network, select In another project (unless you want to peer within the same project).

  8. For Project ID, paste the project ID of the first project (project-A):

{{{ project_0.project_id | "PROJECT ID 1"}}}
  1. For VPC network name, type network-a

  2. Click Create.

On the VPC network peering page, peer-ba now appears in the peering connection list.

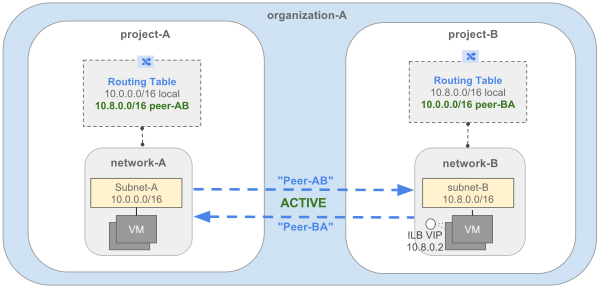
VPC Network Peering becomes ACTIVE, and the networks exchange routes. When the peering moves to an ACTIVE state, Google Cloud sets up traffic flows:

  • Between VM instances in the peered networks: Full mesh connectivity.
  • From VM instances in one network to Internal Load Balancing endpoints in the peered network.

Active Peer-AB and Peer-BA network diagram

The routes to peered network CIDR prefixes are now visible across the VPC network peers. Google Cloud generates these implicit routes for active peerings, and they don't have corresponding route resources.

  1. In the Cloud Shell for project-A, run the following command to list the routes for all VPC networks in project-A:
gcloud compute routes list --project {{{ project_0.project_id }}}

Example output:

NAME NETWORK DEST_RANGE NEXT_HOP PRIORITY default-route-2a865a00fa31d5df network-a 0.0.0.0/0 default-internet-gateway 1000 default-route-8af4732e693eae27 network-a 10.0.0.0/16 1000 peering-route-4732ee69e3ecab41 network-a 10.8.0.0/16 peer-ab 1000

Click Check my progress to verify the objective. Peer network-b with network-a

Task 3. Test connectivity

In this task, you perform a connectivity test between vm-b and vm-a.

Retrieve the internal IP address of vm-a in project-A

  1. In the Google Cloud console, switch to project-A ().

  2. On the Navigation menu (Navigation menu icon), click Compute Engine > VM instances.

  3. Copy the Internal IP address for vm-a.

Ping vm-a from vm-b in project-B

  1. In the Google Cloud console, switch to project-B ().

  2. On the Navigation menu (Navigation menu icon), click Compute Engine > VM instances.

  3. For vm-b, click SSH to launch a terminal and connect.

  4. In the SSH terminal of vm-b, run the following command, replacing <INTERNAL_IP_OF_VM_A> with the internal IP address of vm-a:

ping -c 5

Example output:

PING 10.8.0.2 (10.8.0.2) 56(84) bytes of data. 64 bytes from 10.8.0.2: icmp_seq=1 ttl=64 time=1.07 ms 64 bytes from 10.8.0.2: icmp_seq=2 ttl=64 time=0.364 ms 64 bytes from 10.8.0.2: icmp_seq=3 ttl=64 time=0.205 ms 64 bytes from 10.8.0.2: icmp_seq=4 ttl=64 time=0.216 ms 64 bytes from 10.8.0.2: icmp_seq=5 ttl=64 time=0.164 ms --- 10.8.0.2 ping statistics --- 5 packets transmitted, 5 received, 0% packet loss, time 4065ms rtt min/avg/max/mdev = 0.164/0.404/1.072/0.340 ms

Congratulations!

You learned how to set up VPC Network Peering across projects in Google Cloud.

Next steps / learn more

Google Cloud training and certification

...helps you make the most of Google Cloud technologies. Our classes include technical skills and best practices to help you get up to speed quickly and continue your learning journey. We offer fundamental to advanced level training, with on-demand, live, and virtual options to suit your busy schedule. Certifications help you validate and prove your skill and expertise in Google Cloud technologies.

Manual Last Updated on November 11, 2026

Lab Last Tested November 7, 2026

Copyright 2026 Google LLC. All rights reserved. Google and the Google logo are trademarks of Google LLC. All other company and product names may be trademarks of the respective companies with which they are associated.

Before you begin

  1. Labs create a Google Cloud project and resources for a fixed time
  2. Labs have a time limit and no pause feature. If you end the lab, you'll have to restart from the beginning.
  3. On the top left of your screen, click Start lab to begin

Use private browsing

  1. Copy the provided Username and Password for the lab
  2. Click Open console in private mode

Sign in to the Console

  1. Sign in using your lab credentials. Using other credentials might cause errors or incur charges.
  2. Accept the terms, and skip the recovery resource page
  3. Don't click End lab unless you've finished the lab or want to restart it, as it will clear your work and remove the project

This content is not currently available

We can notify you via email when it becomes available

Great!

We can contact you via email if it becomes available

One lab at a time

Confirm to end all existing labs and start this one

Use private browsing to run the lab

Using an Incognito or private browser window is the best way to run this lab. This prevents any conflicts between your personal account and the Student account, which may cause extra charges incurred to your personal account.




